Data Skimmed: Hacker Attack on Munich University
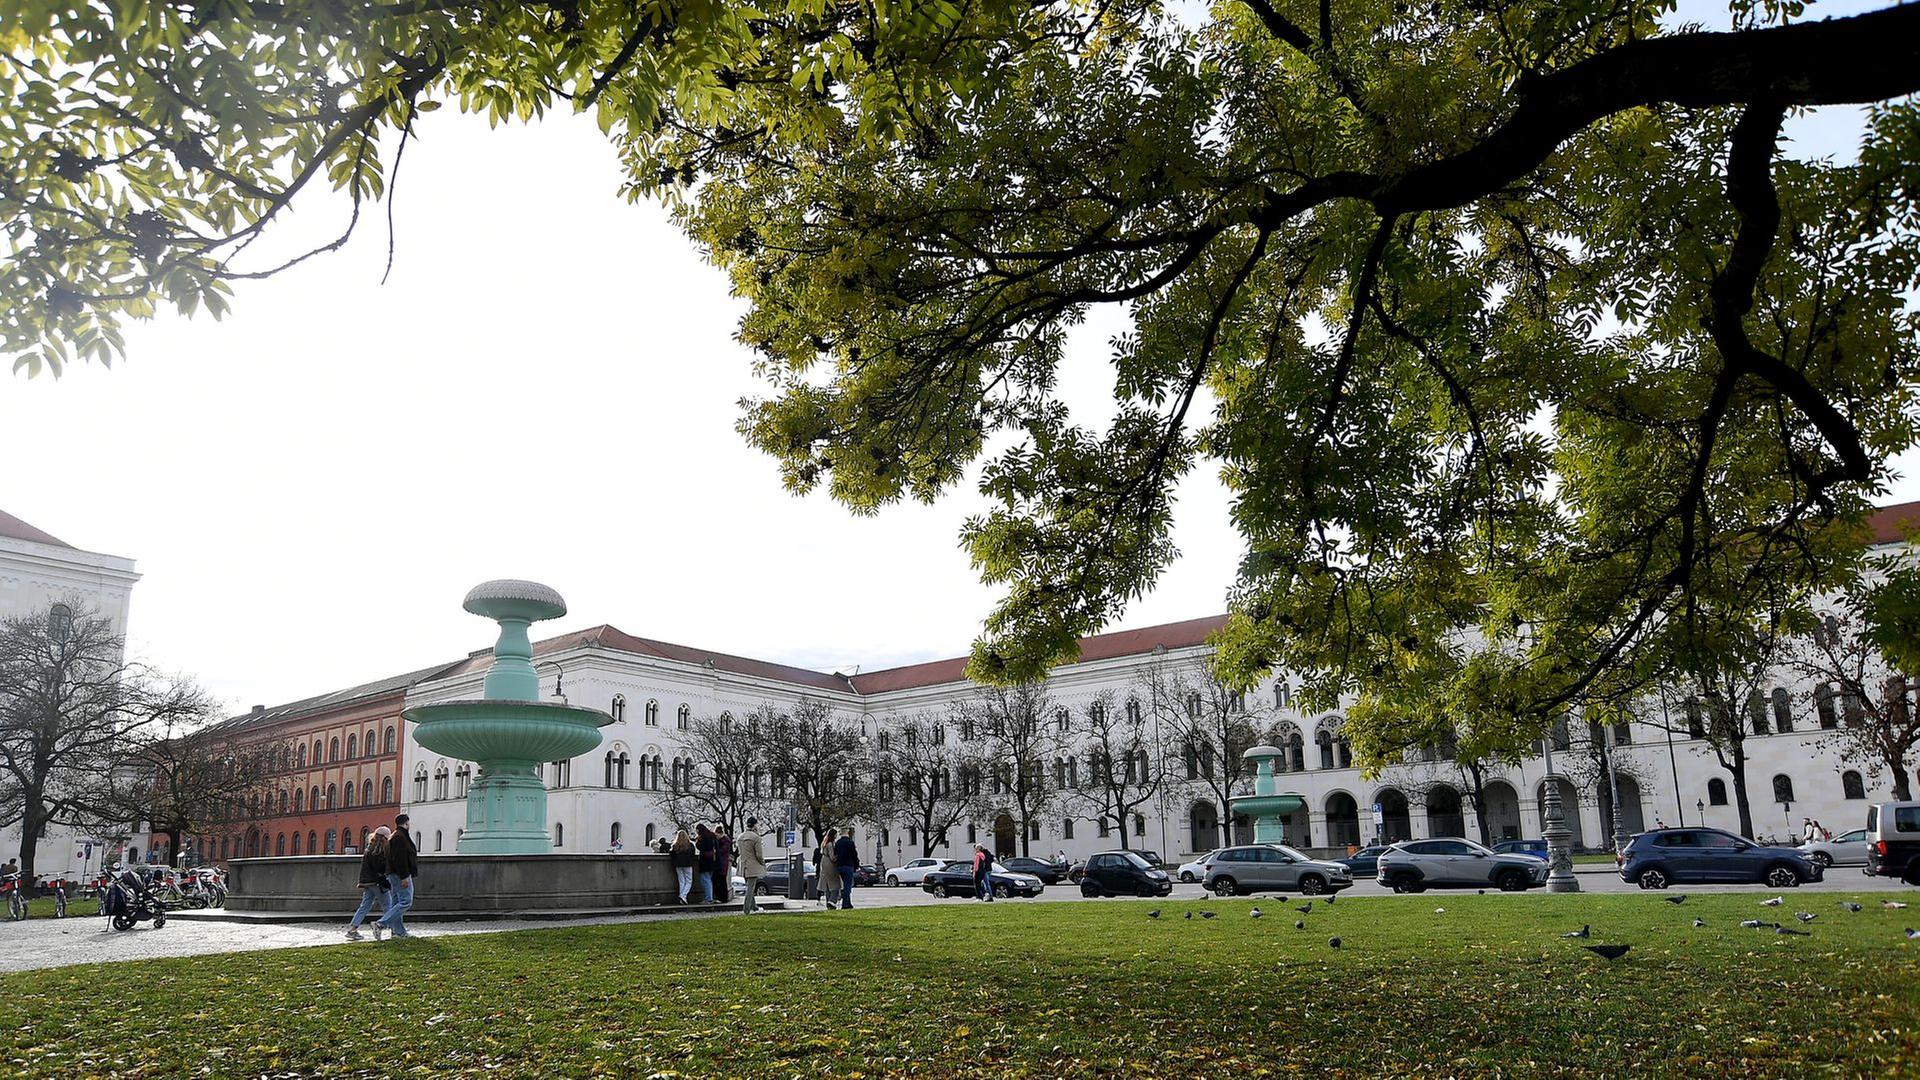
Ludwig Maximilian University in Munich has fallen victim to a hacker attack. The attackers apparently gained access to sensitive student data. The full extent remains unclear.
Just before the start of the new winter semester, the renowned Ludwig Maximilian University Munich reported a hacker attack. Cybercriminals had penetrated the university's IT systems, as stated on its website. There, they allegedly skimmed the personal master data of students related to enrollment at LMU.
Hackers Were Able to View Personal Student Data
According to the university's statement, the compromised information includes sensitive details such as name, date of birth, gender, and place of birth. Additionally, home addresses, telephone numbers, email addresses, and banking details (e.g., IBAN, account holder name) were affected. Information regarding students' health insurance, BAföG numbers, data relating to academic progress, as well as details about previous school or university qualifications were also compromised.
Explicitly not affected are LMU examination records or specific information about course content and individual academic performance. Also noteworthy: according to the statement, any alteration or other manipulation of the data was prevented.
Investigation Still Ongoing
The full extent of the damage currently remains unclear. According to the university, the technical investigation is still ongoing. For this reason, no reliable information can currently be provided regarding the total number of affected individuals, the volume of data, or the time periods involved. The university is working with the relevant investigative and supervisory authorities as well as external specialists — also to ward off further attacks.
The incident was identified last Wednesday. Immediately afterward, the university took countermeasures and shut down the affected system, it was stated. Exactly when the hackers gained access and how long they had it remains unknown.
No Data Published as of Now
Whether data was also stolen cannot yet be conclusively determined. Designated specialists are monitoring relevant dark web portals for any indications relating to the affected information.
LMU states on its website: "Based on current findings, there are no indications that the attacker has published the obtained dataset, intends to do so, or is otherwise misusing it." However, should any indications emerge that the data has been published or otherwise misused, those affected will be contacted immediately.
What Does This Mean for Students?
As LMU further announced, in addition to the enrollment server affected by the incident, several unaffected systems were also proactively shut down as a precaution. As a result, some internal services are temporarily unavailable.
However, academic operations do not appear to be affected. Enrollment is set to resume after a brief interruption starting next week. The affected enrollment deadlines will be extended accordingly, and existing enrollments will remain valid without change. LMU emphasizes that students will not suffer any academic disadvantage as a result of the incident.
LMU Urges Caution
Nevertheless, the university is calling for vigilance and advises following the usual general precautionary measures. These include, among other things, not opening attachments in suspicious emails and not disclosing bank details or passwords.
LMU is also keeping the public informed about the current status of the incident on its website.
That is the European perspective on BR24.
"Here is Bavaria": The BR24 newsletter keeps you informed about the most important news of the day every Monday to Friday at the end of the working day at a glance – concise and delivered directly to your personal inbox. Click here to sign up!
Source: BAYERN 3 News 20.09.2026 - 09:00